Coordinated Grid Drops, Cyber VC and a Mac Cleaner
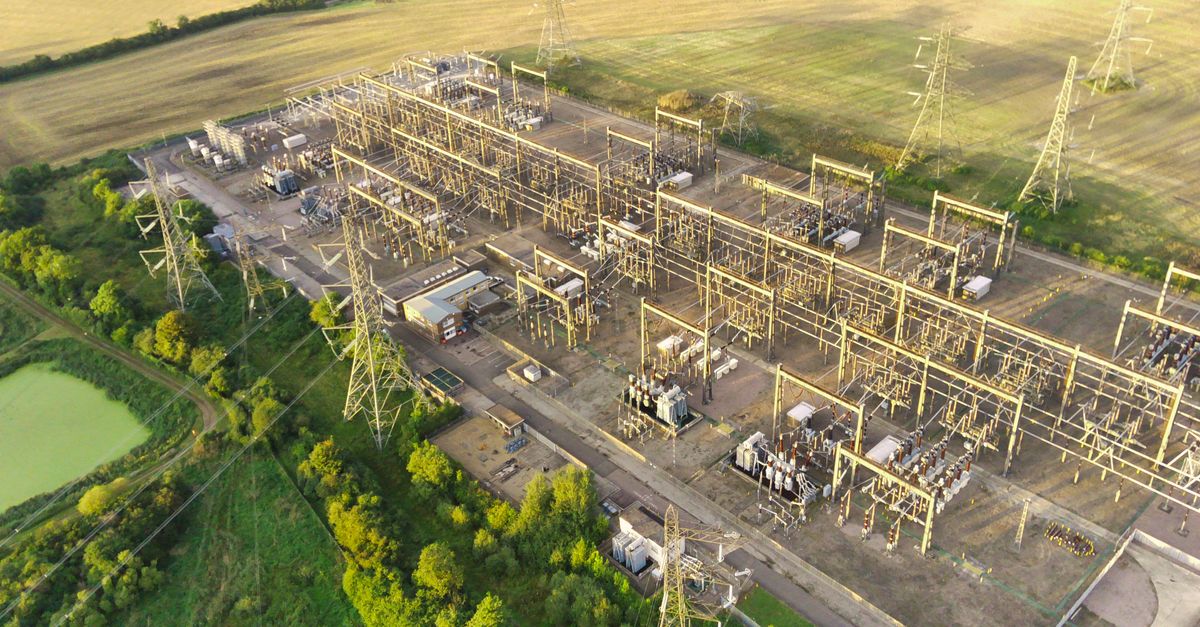
Photo by Altaf Shah on Pexels
Coordinated grid drops finally get a name
Power outages that appeared in lockstep across continents stopped being a mystery last week. A German research team announced they had identified the source of the coordinated drops that have haunted operators for years.
The team, based at a university in Berlin, published a brief note describing how the drops shared a timing signature that pointed to a single trigger. They did not claim a malicious actor, but the fact that the pattern was reproducible gave grid managers a concrete clue to chase. The announcement arrived just as utilities in North America and Europe were scrambling to explain a series of three‑hour blackouts that knocked out data centers and manufacturing lines.
What this means for the grid is simple: operators now have a variable to monitor rather than a black box. In practice that could translate into tighter synchronization checks and a review of the software that schedules load shedding. The research does not solve the engineering challenges of modern grids, but it removes a layer of uncertainty that has cost utilities billions in lost productivity.
Stephen Ward’s $250 million bet on cyber resilience
Former Secret Service agent and ex‑Home Depot CISO Stephen Ward is moving from corporate security to venture capital. Ward announced a second fund for Brightmind Partners, targeting roughly $250 million in capital.
The fund will back startups that promise to harden the digital supply chain, protect critical infrastructure, and deliver more transparent breach response tools. Ward’s background gives him credibility; he spent a decade in federal law‑enforcement cyber work before heading security at a major retailer. His first Brightmind fund already backed a handful of firms that focus on zero‑trust networking and automated threat hunting.
Industry observers note that the timing is deliberate. After the coordinated grid drops were traced, investors have been looking for ways to shore up the cyber‑physical systems that keep power flowing. Ward’s fund could become a conduit for the next generation of grid‑security startups, especially those that blend hardware tamper‑proofing with AI‑driven anomaly detection.
A soldier’s SIM card mistake highlights a broader security gap
A British soldier recently found himself court‑martialed after repeatedly ignoring orders to lock down his mobile device before deployment. The soldier’s SIM card remained active, allowing an adversary to send compromising material that led to a sextortion attempt.
The case surfaced in an Ars Technica report that detailed how the soldier was repeatedly warned to secure his phone, yet he kept the device unlocked. When the blackmail material surfaced, the military prosecuted the soldier for breaching operational security protocols. The court‑martial outcome underscores how personal device hygiene can have career‑ending consequences.
For engineers building secure communications, the story is a reminder that policy enforcement must be coupled with technical controls. Simple device‑lock requirements are easy to ignore; without automated enforcement—such as remote wipe or mandatory encryption—human error can become a vector for espionage or extortion.
An open‑source Mac app that actually frees space
Mac users looking to trim excess storage now have a free alternative to commercial disk cleaners. A community‑maintained utility scans for hidden caches, leftover app junk, and even large offline Apple Intelligence models that sit unused on the drive.
The tool, released under an open‑source license, safely deletes files that are not needed for everyday operation. Early adopters report reclaiming several gigabytes of space without the bloat that often accompanies paid cleaners. Because the app is transparent about what it removes, users can audit the process before committing to deletion.
Beyond freeing storage, the app serves as a case study in how open‑source projects can fill niches that big vendors overlook. Apple’s own cleanup utilities remain hidden in system settings, and third‑party solutions frequently bundle adware. This utility sidesteps that model, offering a lean, community‑driven approach that resonates with power users who value control over their machines.
What to watch next
Grid operators will be monitoring whether the German team’s findings lead to measurable reductions in coordinated outages. Keep an eye on any regulatory filings that reference the new research, as they could signal industry‑wide adoption of new monitoring standards. In the cyber‑investment space, Ward’s Brightmind fund will publish its first portfolio in the coming quarter; the composition of that portfolio will hint at which grid‑security technologies are gaining traction. Meanwhile, the British military is expected to tighten device‑lock enforcement after the recent court‑martial, possibly rolling out automated compliance tools. Finally, the open‑source Mac cleaner will likely see contributions that expand its scope to other Apple‑specific caches, so watch the project’s repository for major releases.
Related Articles
AI race, data breach, and new browsing tool raise tech tension
OpenAI and Anthropic's AI speed, a CareCloud breach, pricey phone cases, and Gemini Spark's Chrome browsing update illustrate rising tech stakes.
IOCCC 2025 Winners Show Low-Level Shift Amid AI, Serverless
The 2025 IOCCC results, a new tokenomics study, and a serverless platform prototype illustrate evolving tensions in programming practice and research.
Codex hack, 100k ALPRs, brain creatine, cancer pill, backpressure
A look at a Codex sudo workaround, Deflock's 100k ALPR map, creatine's brain boost, a pancreatic cancer pill that doubles survival, and why backpressure matters.