AI agents get a driver’s seat as funding, security
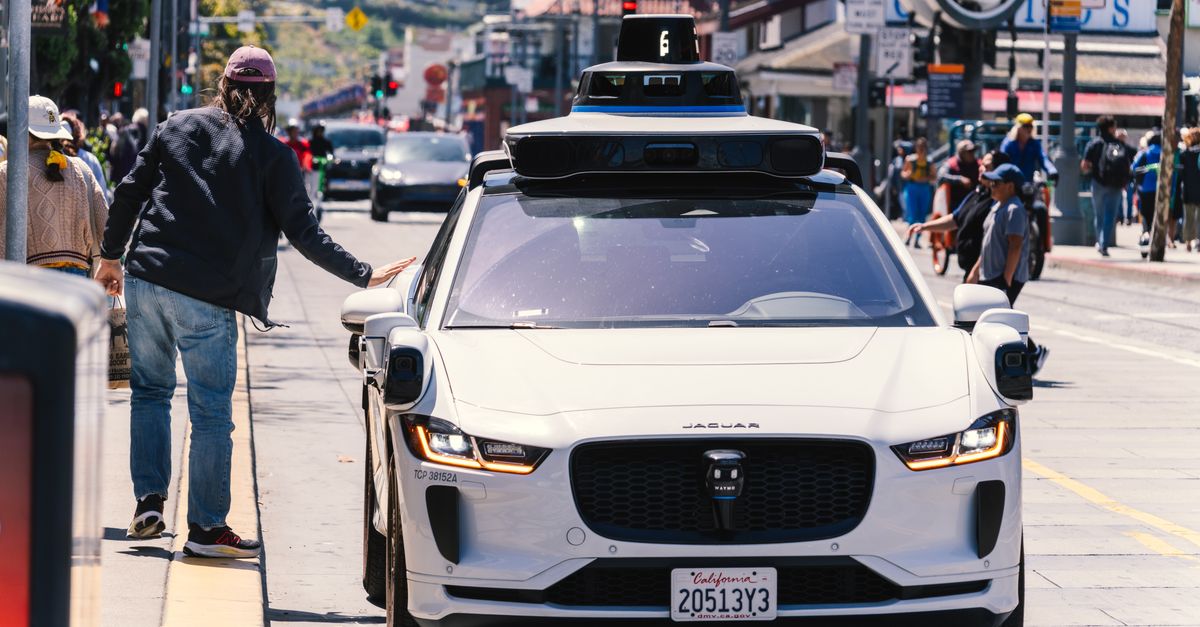
Photo by Abhishek Navlakha on Pexels
Plurai is adapting self‑driving car training methods to tame AI agents. The startup argues that end‑to‑end models, which taught autonomous vehicles to navigate streets, can be repurposed for agents that operate in probabilistic, unpredictable environments.
TechCrunch reports that Plurai’s system treats an agent like a driver: it feeds raw sensor streams into a single neural pipeline that outputs actions. The approach sidesteps modular pipelines that split perception, planning, and control. By keeping the model monolithic, Plurai hopes to reduce latency and improve robustness when the world throws curveballs.
The tradeoff is clear. End‑to‑end training assumes the training distribution covers the deployment space. Real‑world interactions remain stochastic, and a single network can hide failure modes that modular debugging would expose. Critics ask whether safety guarantees can survive the black‑box nature of large models. Plurai acknowledges the gap and promises a validation suite, but the question of verifiable safety remains open.
Radical Numerics unveiled a model that scans biological data for signatures of both natural pathogens and AI‑engineered threats. WIRED notes that the system runs entirely offline, eliminating the need for an internet connection during analysis.
The model claims to flag suspicious sequences in seconds, a speed that could matter in a containment scenario. By operating without external queries, the tool avoids exposing sensitive data to cloud services. The promise is a rapid, privacy‑preserving first line of defense against bio‑AI weaponization.
However, the claim rests on limited testing. The paper does not disclose detection rates against novel synthetic constructs, nor does it compare performance to established bioinformatics pipelines. Without transparent benchmarks, regulators and labs will have to weigh the convenience against unknown false‑positive or false‑negative rates. The community will be watching for independent validation.
TSMC announced a $1 billion investment split between Anthropic and OpenAI, according to Ars Technica. The chipmaker’s capital infusion arrives as the AI boom’s financing loops back into the hardware layer that powers large models.
The move underscores the growing interdependence of silicon and software. TSMC’s foundries supply the GPUs and TPUs that run Anthropic’s Claude and OpenAI’s ChatGPT. By staking cash directly in the model developers, TSMC secures demand for its next‑generation process nodes.
The financing also signals confidence amid a wobbling AI trade environment. Recent market turbulence has prompted some investors to pull back, yet TSMC’s bet suggests that the hardware side still expects sustained growth. The real test will be whether the funded models can translate into volume orders for the latest chips, or whether a slowdown in AI spending will leave TSMC with excess capacity.
DeepMind completed a four‑week effort that mathematically verified core components of the Signal messaging app, as reported by Ars Technica. The verification proved that certain cryptographic protocols meet their formal specifications, a step toward proving end‑to‑end security.
Formal verification has traditionally been too costly for large codebases. DeepMind’s experiment shows that AI‑driven proof assistants can automate large parts of the process, shrinking a months‑long manual audit into weeks. The result hints that future security audits could become routine rather than exceptional.
Skeptics note that the verified parts represent only a fraction of Signal’s total code. Extending the technique to the entire stack will demand more tooling and expertise. Moreover, verification does not guarantee the absence of implementation bugs outside the mathematical model. The industry will need to balance the speed gains against the scope limits of current AI‑assisted proof systems.
ByteDance is reportedly developing its own AI agent to compete with Meta’s Muse, Engadget reports. The Chinese internet giant aims to leverage its massive user data and recommendation infrastructure to power a conversational assistant.
If ByteDance succeeds, it could add a new voice to the crowded agent market, which already includes OpenAI’s ChatGPT, Google’s Gemini, and Anthropic’s Claude. ByteDance’s advantage may lie in seamless integration with its short‑form video platforms, potentially enabling cross‑modal interactions.
The venture raises questions about data privacy and cross‑border regulation. ByteDance must navigate Chinese cybersecurity rules while serving a global audience. The agent’s performance will also be measured against existing models that already benefit from years of research. Observers will track launch timelines and any partnership announcements that could accelerate development.
What to watch
Plurai’s next public benchmark will reveal whether end‑to‑end training can meet safety standards demanded by regulators. Radical Numerics plans a peer‑reviewed study of its pathogen detector later this year; the results will set a baseline for AI‑based biosecurity tools. TSMC’s investment milestones with Anthropic and OpenAI will be disclosed in quarterly earnings, offering a gauge of hardware demand. DeepMind intends to publish a broader verification suite for Signal in the coming months, testing the scalability of AI‑assisted proofs. ByteDance’s agent rollout date remains vague, but any beta release will expose how the company balances user data with emerging privacy norms.
Related Articles
AI agents multiply across apps as platforms wrestle with safety
Instinct, TikTok, HackerRank and OpenAI roll out new AI agents while researchers flag security risks and regulators demand transparency.
GitHub's New PR Dashboard and a Claude Code Leak Raise Fresh
GitHub rolls out a public‑preview PR overview page while a Claude Code feature leaked 1,122 passwords, sparking security concerns.
Samsung trackers, AI cost cuts and tech investigations
A roundup of new hardware, open‑source tools, AI cost breakthroughs, security research, and regulatory pressure on big tech.